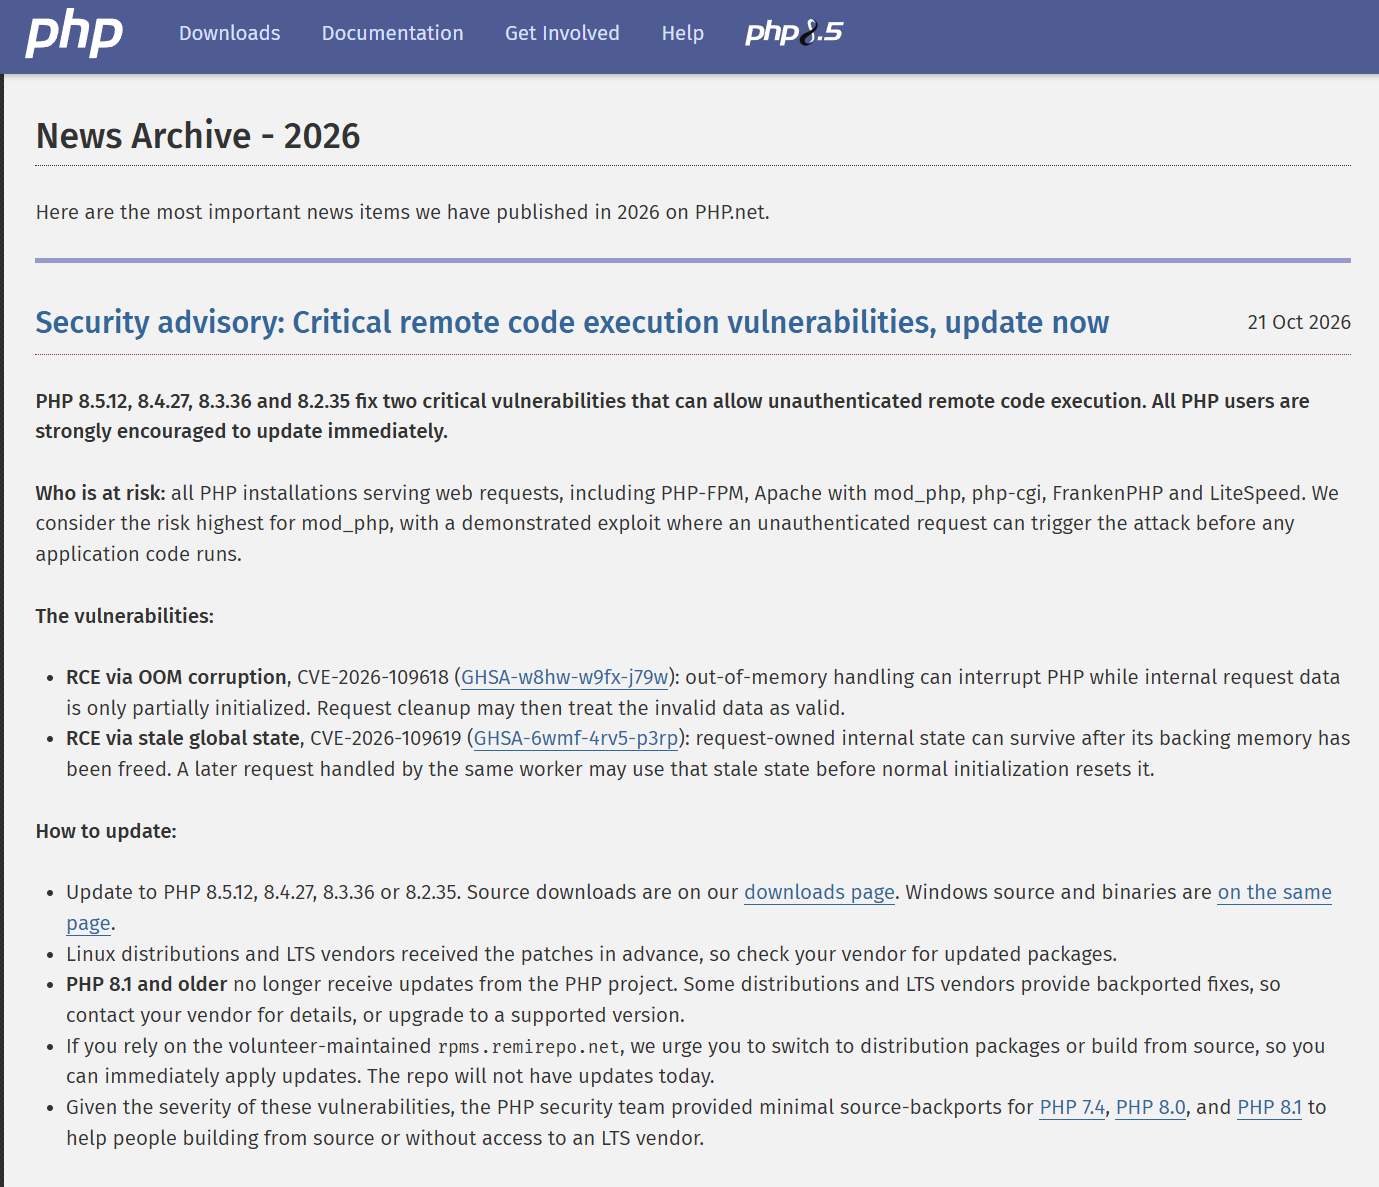
PHP warned October 20 of two critical remote code execution flaws, both rated CVSS 9.2, scheduled for release October 21 at 2 p.m. UTC. Details and an exploit tool called PHP2Shell leaked overnight. Cloudflare reported early attacks. CERT-EU and others told operators unable to patch fast to take sites offline. Dutch government portals, Japanese services and others went dark as a precaution. PHP released 8.5.12, 8.4.27, 8.3.36 and 8.2.35 on October 21 fixing CVE-2026-109618 and CVE-2026-109619. The bugs allow unauthenticated code execution, worst on mod_php. PHP 8.1 and older get no official fix. PHP said “There are no complete mitigations, updating is the only safe choice.”
*FINLAND SHUTS STATE INTERNET SERVICES OVER PHP FLAWS
*NETHERLANDS CYBERSECURITY AGENCY TAKES WEBSITE OFFLINE OVER PHP FLAWS
*FRANCE TEMPORARILY TAKES PREFECTURE WEBSITES OFFLINE PENDING PHP FIX: MINISTRY https://t.co/mi9GbPXmOK
— *Walter Bloomberg (@DeItaone) October 21, 2026
BREAKING: Governments in Europe are shutting down their websites because of critical flaws in PHP, the language behind millions of websites.
Finland, the Netherlands and France have taken government websites offline, including the Dutch cybersecurity agency's own site. pic.twitter.com/pB9VNatHi9
— Bull Theory (@BullTheoryio) October 21, 2026
https://www.php.net/archive/2026.php
https://lwn.net/Articles/1102014/
Got a news tip or correction? Let us know
If you got something out of this, please chip in to keep this site running, or subscribe to go ad-free.
31 views